Salem, OregonFractional CISO & security program leadership

Jared Gross

Security Executive | Fractional CISO | Cybersecurity Program Leadership

I help growing and regulated organizations bring structure, ownership, and executive direction to cybersecurity — aligning leadership, IT teams, security providers, risk, and compliance around a security program that actually moves.

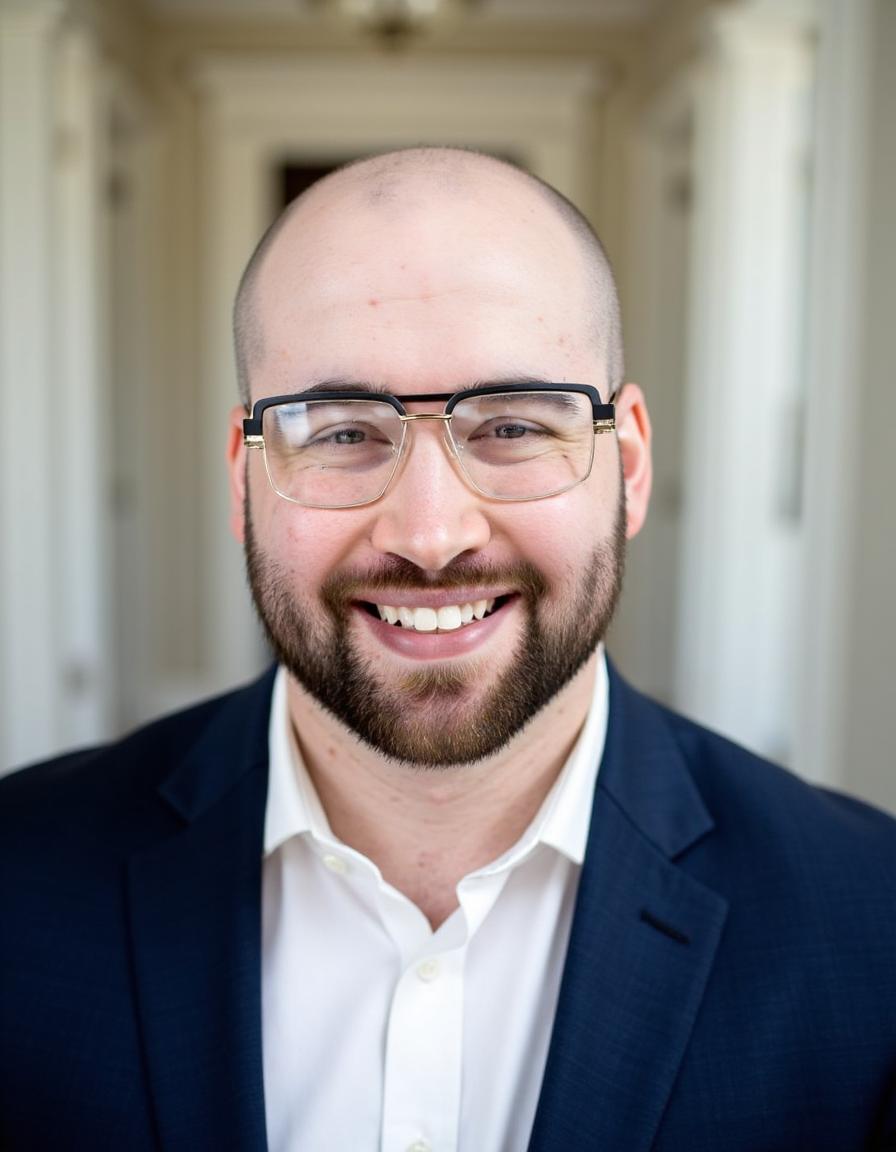
Portrait of Jared Gross
N 44.94°W 123.04°

Security leadership for environments where risk, recovery readiness, and executive decision-making cannot drift.

Years in IT & cybersecurity
10+
Environments
Fortune 500 · Healthcare · Regulated
Portfolio led
$3M+
Focus areas
Cyber resilience · Security governance · AI governance

When organizations bring me in

  • 01

    No clear security owner

    Security is spread across the CTO, IT, MSPs, vendors, compliance tools, and whoever has time. I establish the operating layer that connects them.

  • 02

    Enterprise pressure is increasing

    Customers, insurers, auditors, investors, or leadership are asking harder security questions than the current operating model can answer.

  • 03

    Security work keeps stalling

    The findings are known. The tools exist. What is missing is prioritization, ownership, sequencing, and executive follow-through.

  • 04

    AI is moving faster than governance

    Teams are adopting new AI capabilities while data handling, acceptable use, vendor accountability, and executive decision-making lag behind.

  • 05

    An incident or resilience concern changed the conversation

    Leadership needs someone who can turn technical risk and recovery requirements into an executable program.

  • Recognize your environment?

    These are the conditions where a security leadership layer changes the outcome.

    Start a conversation

If an audit, recovery initiative, contract review, or operationally critical program is already under pressure, let's talk before the situation becomes harder to unwind.

Discuss security leadership

Experience across

  • Fortune 500
  • Healthcare
  • Public Sector
  • Manufacturing
  • SaaS
  • Gaming Infrastructure

01 — Summary

Executive summary

Security executive and technology leader with 10+ years operating across cybersecurity, infrastructure, cloud, resilience, automation, AI governance, and complex technical programs.

My strongest work sits at the intersection of security and the business: translating technical risk into decisions, establishing ownership, creating executable roadmaps, aligning internal teams and providers, and giving leadership a clear picture of where the security program actually stands.

Unlike a purely compliance-oriented security advisor, I have spent my career inside the technical environments security programs depend on — infrastructure, cloud, identity, automation, recovery, engineering, and enterprise delivery. That work spans Fortune 500, healthcare, public sector, gaming, SaaS, and regulated environments, including Nike, Bungie, Salesforce, Rockwell Automation, Resource Data, and the Oregon Health Authority.

Recent emphasis

  • 01

    Security Program Leadership

    Cybersecurity strategy, risk governance, security roadmaps, executive reporting, and vendor accountability.

  • 02

    Cyber Resilience & Incident Governance

    Ransomware readiness, isolated recovery, disaster recovery, business continuity, and executive tabletop programs.

  • 03

    Identity, Data & Cloud Security

    IAM/PAM, Zero Trust, least privilege, DLP and data classification, insider risk, and cloud security governance.

  • 04

    AI Governance & Emerging Technology Risk

    NIST AI RMF, acceptable use policy, LLM oversight, vendor accountability, privacy boundaries, and responsible AI adoption.

02 — Operating model

How I lead security programs

Clarify. Align. Prioritize. Sustain.

  1. Clarify

    Understand the actual security picture before changing it. Systems, exposure, ownership, obligations, and what is genuinely fragile.

  2. Align

    Make ownership, decision rights, providers, and responsibilities legible — so nothing material sits in the gap between teams.

  3. Prioritize

    Focus leadership and technical effort on what matters most, sequenced against real constraints rather than framework order.

  4. Sustain

    Establish the cadence, visibility, and accountability that keeps the program moving after the initial push.

This operating model became the foundation of the Frontier Security Office.

03 — What I deliver

Selected achievements & focus

Programs delivered under audit, compliance, and operational pressure — and the domains where I lead day-to-day.

  • A

    AI Governance & Cloud Security

    Built and led enterprise cloud security and AI governance programs aligned to NIST CSF, NIST AI RMF, CMMC, and SOC 2 — enabling responsible adoption of generative AI within regulated environments.

  • B

    Generative AI Policy & Platform Governance

    Developed AI acceptable use policies and governance frameworks supporting healthcare, small, and mid-market organizations adopting Microsoft Copilot, ChatGPT, Claude, and Perplexity.

  • C

    Cyber Resiliency & Recovery Modernization

    Led enterprise cyber resiliency and recovery modernization initiatives focused on ransomware recovery readiness, isolated recovery environments, operational resilience governance, and executive tabletop exercises.

  • D

    Global WAF Migration & PMO Governance

    Directed Nike's global WAF migration to Akamai across 200+ domains — reducing critical vulnerabilities by 40% — and built the PMO governance framework standardizing cadence, reporting, and delivery across the global cloud/security portfolio.

Where I operate

Focus areas

Domains where I lead, advise, and deliver across enterprise and regulated environments.

  • 01AI Governance
  • 02Identity & Access Governance
  • 03Operational Resilience
  • 04Cybersecurity Program Leadership
  • 05Cloud Security
  • 06Generative AI Risk Management
  • 07Recovery Readiness
  • 08Executive Reporting

04 — Experience

Experience

10+ years across IT, infrastructure, cloud, cybersecurity, and AI governance — Fortune 500, healthcare, gaming, public sector, and military environments.

  1. 01

    Frontier Security Office

    Founder & Security Executive | Fractional CISO

    Jul 2025 — PresentSalem, OR · Remote

    Founded and lead an independent practice providing embedded IT, security, AI governance, and operational resilience leadership for healthcare and regulated organizations. Serve as vCIO/vCISO advisor to the CFO of one of Oregon's largest home health agencies — supporting technology roadmapping, governance, risk prioritization, vendor accountability, and executive decision-making across IT, security, and compliance. Deliver Fortune 500 operating discipline sized for organizations without Big-Four overhead.

  2. 02

    Rockwell Automation

    Cybersecurity Program Management Lead

    Sep 2025 — PresentOregon · Remote

    Lead complex, cross-functional IT and cybersecurity programs from strategy through execution — owning planning, roadmaps, milestones, dependencies, risk, and delivery across multiple enterprise workstreams. Promoted from contract senior technical PM to full-time program management lead. Serve as the go-to lead for at-risk initiatives, restoring delivery governance, resolving cross-functional blockers, and rebuilding stakeholder confidence across ransomware recovery, isolated recovery environments, disaster-recovery validation, privileged access, data protection, and Zero Trust. Build delivery capacity by defining resource needs, hiring and onboarding contractors and PMs, and overseeing performance against scope, timelines, budgets, and quality. Establish program governance, executive reporting, decision frameworks, and escalation paths that improve delivery predictability, and facilitate operational-resilience planning through executive tabletop exercises and continuity governance aligned to enterprise risk priorities.

  3. 03

    Resource Data

    Senior Technical Program Manager & Cloud / AI Security Lead

    Aug 2023 — Aug 2025Portland, OR

    Served as acting Director of IT / director-level technology lead, overseeing IT operations, roadmap planning, and delivery coordination across 15 systems engineers, architects, and technical project managers. Directed a $3M+ portfolio across cloud security, application modernization, and enterprise technology governance, and led the migration of critical applications to AWS with zero downtime. As AI Security Lead, drove enterprise AI adoption and platform evaluation (Microsoft Copilot, ChatGPT, Claude, Perplexity) aligned to NIST AI RMF, partnering with Finance, Operations, and IT leadership on risk, spend, compliance, and vendor accountability.

  4. 04

    Bungie

    Automation & AI Engineering Lead

    Mar 2022 — Jun 2023Bellevue, WA

    Led automation and AI-driven security programs supporting global threat detection, infrastructure reliability, and scalable operations. Partnered with executives and technical leaders on automation strategy, investment priorities, and risk reduction. Built Python, Perl, and PowerShell tooling that eliminated 500+ hours of manual work annually, and founded and scaled the Veteran Vanguard ERG to 40+ members.

  5. 05

    Nike

    PM / Engineering Lead — Cloud & Infrastructure Automation

    Jun 2019 — Sep 2021Beaverton, OR

    Led global infrastructure automation and security projects impacting $1M+ in operations. Oversaw a multi-region enterprise WAF rollout across 200+ domains and coordinated a global CDN migration — improving security posture, standardization, resilience, and audit readiness. Delivered automated certificate lifecycle processes and executive KPI dashboards for compliance visibility, risk tracking, and milestone management.

  6. 06

    Nike

    PMO Lead — Strategic IT Projects

    Jul 2018 — Jun 2019Beaverton, OR

    Built and operationalized a PMO governance framework supporting multi-cloud security and infrastructure programs across AWS, Azure, GCP, and Alibaba Cloud — establishing governance standards, delivery cadence, and runbooks supporting audit stability and predictable execution.

  7. 07

    Salesforce

    Technical Project Lead — Automation & Security

    Aug 2017 — Jul 2018Indianapolis, IN

    Automated LDAP, CRL, and network security monitoring, reducing manual workload by 200+ hours annually. Directed KPI dashboard development and cross-team delivery supporting NIST and SOC 2 audit readiness, operational tracking, and leadership visibility.

  8. 08

    Oregon Health Authority

    Information Systems Analyst — SecOps

    Dec 2015 — Aug 2017Portland, OR

    Led penetration testing, vulnerability assessments, remediation coordination, incident response, and security training in a regulated healthcare environment — supporting HIPAA, NIST, and Oregon state compliance mandates across technology and operations stakeholders.

  9. 09

    Army National Guard

    Squad Leader — Combat Engineer

    May 2013 — Apr 2017Dallas, OR

    Led a combat engineer squad executing high-risk missions — discipline, coordination, and operational risk management under pressure.

05 — Representative initiatives

Representative operational initiatives

Sanitized examples of the operational environments and initiatives I lead inside. Detail and additional context available on request.

  • Enterprise Cyber Resiliency & Recovery Modernization

    Led enterprise resiliency initiatives across ransomware recovery readiness, isolated recovery environments, executive tabletop coordination, and operational recovery governance.

    Aligned infrastructure, identity, security, vendors, and leadership around measurable recovery objectives and continuity planning.

    Focus areas

    • Operational Resilience
    • Recovery Governance
    • Executive Coordination
    • Cyber Recovery

    Why it mattered

    Reduced operational uncertainty during recovery planning across infrastructure and security stakeholders.
  • Global WAF & Infrastructure Security Modernization

    Directed enterprise web application firewall modernization across 200+ domains, improving security posture and reducing critical vulnerabilities at global scale.

    Coordinated infrastructure, security, engineering, and vendor stakeholders while protecting service continuity across enterprise-facing platforms.

    Focus areas

    • Cloud Security
    • Infrastructure Governance
    • Risk Reduction
    • Operational Delivery

    Why it mattered

    Standardized security governance across global infrastructure without disrupting enterprise-facing services.

  • Enterprise Security PMO Governance Framework

    Built and operationalized governance structures supporting multi-cloud security and infrastructure initiatives across AWS, Azure, GCP, and Alibaba Cloud.

    Established executive reporting cadence, dependency management, and delivery governance supporting audit stability and predictable execution.

    Focus areas

    • PMO Governance
    • Executive Reporting
    • Multi-Cloud Coordination
    • Portfolio Governance

    Why it mattered

    Improved governance visibility and delivery coordination across large-scale modernization efforts.

  • AI Governance & Operational Oversight Program

    Led oversight initiatives supporting enterprise AI adoption within regulated and operationally sensitive environments.

    Focused on intake processes, acceptable use guidance, vendor accountability, and alignment to NIST CSF, HIPAA, and enterprise governance expectations. Designed intake and evaluation criteria for LLM-based tools — including output quality review, bias considerations, and operational monitoring requirements — enabling teams to adopt generative AI with defensible release criteria.

    Focus areas

    • AI Governance
    • LLM Evaluation
    • Operational Monitoring
    • Vendor Accountability

    Why it mattered

    Established defensible AI oversight where adoption pressure was already outrunning policy.

  • Privileged Access & Identity Modernization

    Oversaw privileged access modernization across least-privilege enforcement, endpoint privilege management, and service account governance.

    Aligned engineering, infrastructure, and security operations to Zero Trust principles and operational accountability standards.

    Focus areas

    • IAM / PAM
    • Zero Trust
    • Identity Governance
    • Risk Reduction

    Why it mattered

    Reduced identity risk exposure while strengthening operational accountability across regulated environments.

  • Healthcare Governance & Audit Readiness Program

    Supported healthcare organizations navigating audit readiness, AI oversight, vendor accountability, and continuity risk across distributed care environments.

    Work spanned governance assessments, BAA review, policy alignment, and operational ownership mapping tied to real staffing and care delivery constraints. Developed AI oversight frameworks for healthcare organizations evaluating Microsoft Copilot, ChatGPT, and similar platforms — including acceptable use policy, vendor accountability, and PHI boundary controls.

    Focus areas

    • Healthcare Governance
    • HIPAA / HITECH
    • HITRUST
    • PHI Boundary Controls

    Why it mattered

    Established operational accountability structures for audit-sensitive healthcare environments.

  • Enterprise Data Protection & DLP Governance

    Coordinated data protection initiatives across DLP governance, sensitive data classification, insider-risk visibility, and M365 information protection.

    Improved operational visibility into sensitive data handling while supporting compliance and operational risk reduction.

    Focus areas

    • DLP Governance
    • Data Protection
    • Insider Risk
    • Information Governance

    Why it mattered

    Brought operational visibility to sensitive data flows previously governed by assumption.

  • Operational Scale

    Programs and environments spanning:

    • Fortune 500 enterprise environments
    • Healthcare and public sector organizations
    • Multi-million-dollar security and infrastructure initiatives
    • Global infrastructure modernization efforts
    • Enterprise recovery and operational resiliency programs
    • Multi-cloud governance across AWS, Azure, GCP, and Alibaba Cloud
    • Cross-functional coordination across executives, engineering, security, operations, and vendors
    • Audit-sensitive and operationally critical delivery environments

These are representative operational environments and initiatives — not a complete portfolio. Specifics are sanitized to respect the confidentiality of the organizations involved.

06 — Security leadership domains

Where I operate.

The leadership, security, and assurance domains I lead across — supported by the technical foundation underneath them.

  • Executive Security Leadership

    • Cybersecurity Strategy
    • Risk Governance
    • Security Roadmaps
    • Executive & Board Reporting
    • Security Program Management
    • Vendor Accountability

    The security-leadership layer: setting direction, making risk legible to executives, and holding internal teams and providers accountable to a single plan.

  • Security Domains

    • IAM / PAM
    • Cloud Security
    • Data Protection
    • Cyber Resilience
    • Incident Governance
    • Third-Party Risk
    • Vulnerability Management

    Program leadership across privileged access, cloud exposure, information protection, cyber recovery, and incident readiness where exposure cannot drift.

  • Network & Infrastructure Security

    • Zero Trust
    • Network Security Architecture
    • Segmentation & Secure Zones
    • Firewalls, WAF, IDS/IPS
    • NAC & Secure DNS
    • SIEM, Logging & Detection
    • Secure Hybrid Infrastructure

    Architecture and boundary protection: enterprise WAF across 200+ domains, segmentation, secure admin access, and the monitoring that proves controls are working.

  • Assurance & Governance

    • SOC 2
    • HIPAA / HITECH
    • HITRUST
    • CMMC
    • ISO 27001
    • NIST CSF
    • NIST AI RMF
    • AI Governance
    • Customer Assurance

    Audit readiness, control mapping, customer security questionnaires, and AI oversight across healthcare, public sector, and regulated environments.

  • Technical Foundation

    • AWS
    • Azure
    • GCP
    • Microsoft 365
    • Okta / Azure AD
    • CrowdStrike
    • Splunk
    • Qualys / Tenable
    • Cloudflare / Akamai
    • Terraform
    • Python
    • PowerShell
    • ServiceNow

    The engineering and operations background behind the leadership work — why technical teams engage rather than route around the security conversation.

  • Leadership Above the Technical Stack

    A fractional CISO should not become another technical vendor competing with the client's IT organization. The security-leadership layer sets direction, establishes priorities, makes risk legible, and coordinates execution — while internal IT, MSPs, MSSPs, platforms, and specialists remain responsible for their technical domains.

    Focused on

    • Vendor-neutral direction
    • Clear ownership boundaries
    • Coordinated execution
    • Defensible outcomes under pressure

AI-native security leadership

Automate the administration. Keep the judgment.

Modern security programs should use AI to eliminate administrative work without outsourcing judgment.

Increasingly automated

  • Evidence organization
  • Reporting preparation
  • Control mapping
  • Meeting administration
  • Assurance workflows
  • Program telemetry

Remains human

  • Material risk decisions
  • Prioritization
  • Executive communication
  • Incident leadership
  • Accountability

Leadership thesis

Security leadership should have gravity.

When something material happens, the organization should know who is bringing the room together, what needs to be decided, and what happens next.

Technical teams should be able to raise risk early. Executives should be able to get a straight answer about where the program stands. Vendors should know what they own. Decisions should have owners. Priorities should survive contact with reality.

My role is to create that operating clarity — especially when the environment gets complicated.

07 — How I operate

The operating posture

A few principles that shape how I lead programs and work with teams.

“Operational resilience is built before it is tested. Everything I lead is shaped by that one idea.”
JGOperating principle
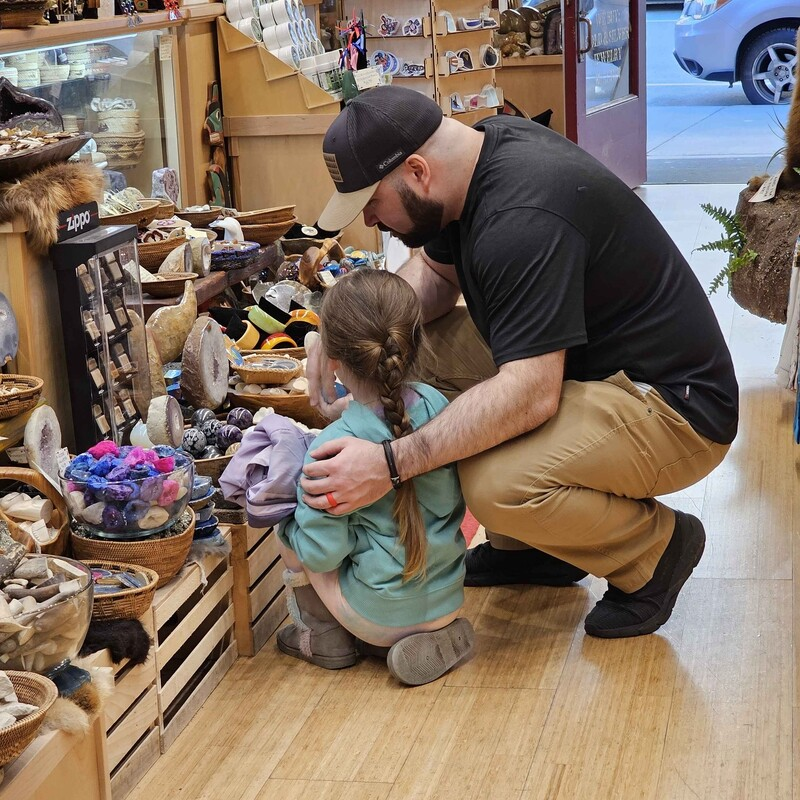
Jared crouched beside his daughter in a rock and mineral shop, looking at stones together
Why this workPacific Northwest

The systems I help protect carry real consequences for real people — patients, families, and communities depending on organizations that have to keep operating, no matter what.

  1. 01

    Calm under pressure.

    Stabilize the room before stabilizing the program. Decisions improve when the operating tempo does.

  2. 02

    Clarity over theater.

    Status reports should describe reality. Reporting that survives audit also survives operations.

  3. 03

    Alignment before acceleration.

    Executives, engineers, vendors, and security all need the same picture before speed creates value.

  4. 04

    Governance built for real conditions.

    Cadence, ownership, and escalation paths designed for outages, audits, and quarter-end — not just kickoff decks.

  5. 05

    Measurable resilience over checkbox activity.

    Recovery readiness, control efficacy, and operational risk reduction — the metrics that hold up when something actually happens.

08 — Founder

Security leadership without building the department.

I founded Frontier Security Office to solve a problem I kept seeing across organizations of very different sizes: security activity existed everywhere, but nobody owned the program as a whole.

Frontier provides managed security leadership for growing organizations — combining fractional CISO judgment, security program management, governance, assurance, and roadmap ownership while working alongside internal IT teams and technical security providers.

My role: Founder & Security Executive.

Where the layer sits

Leadership

Frontier Security Office

Internal IT · MSP / MSSP · Security platforms · Specialists

What Frontier owns

  • 01Fractional CISO leadership
  • 02Security program management
  • 03Governance & risk prioritization
  • 04Assurance & audit readiness
  • 05Security roadmap ownership
Explore Frontier

09 — Contact

Get in touch

For fractional security leadership, executive advisory, strategic partnerships, speaking, or other security leadership conversations.

Credentials

Certifications & clearances

Active and prior credentials supporting governance, delivery, and trusted operational work.

  • CISSP

    In progress

    Certified Information Systems Security Professional

  • CISM

    In progress

    Certified Information Security Manager

  • CSM

    Active · Exp. 2027

    Certified ScrumMaster · Scrum Alliance

  • U.S. Army

    Inactive

    Former Secret Security Clearance

Evaluating security leadership for your organization?

Start with a conversation, or review the full CISO resume — security strategy, secure infrastructure, governance, and control domains.